
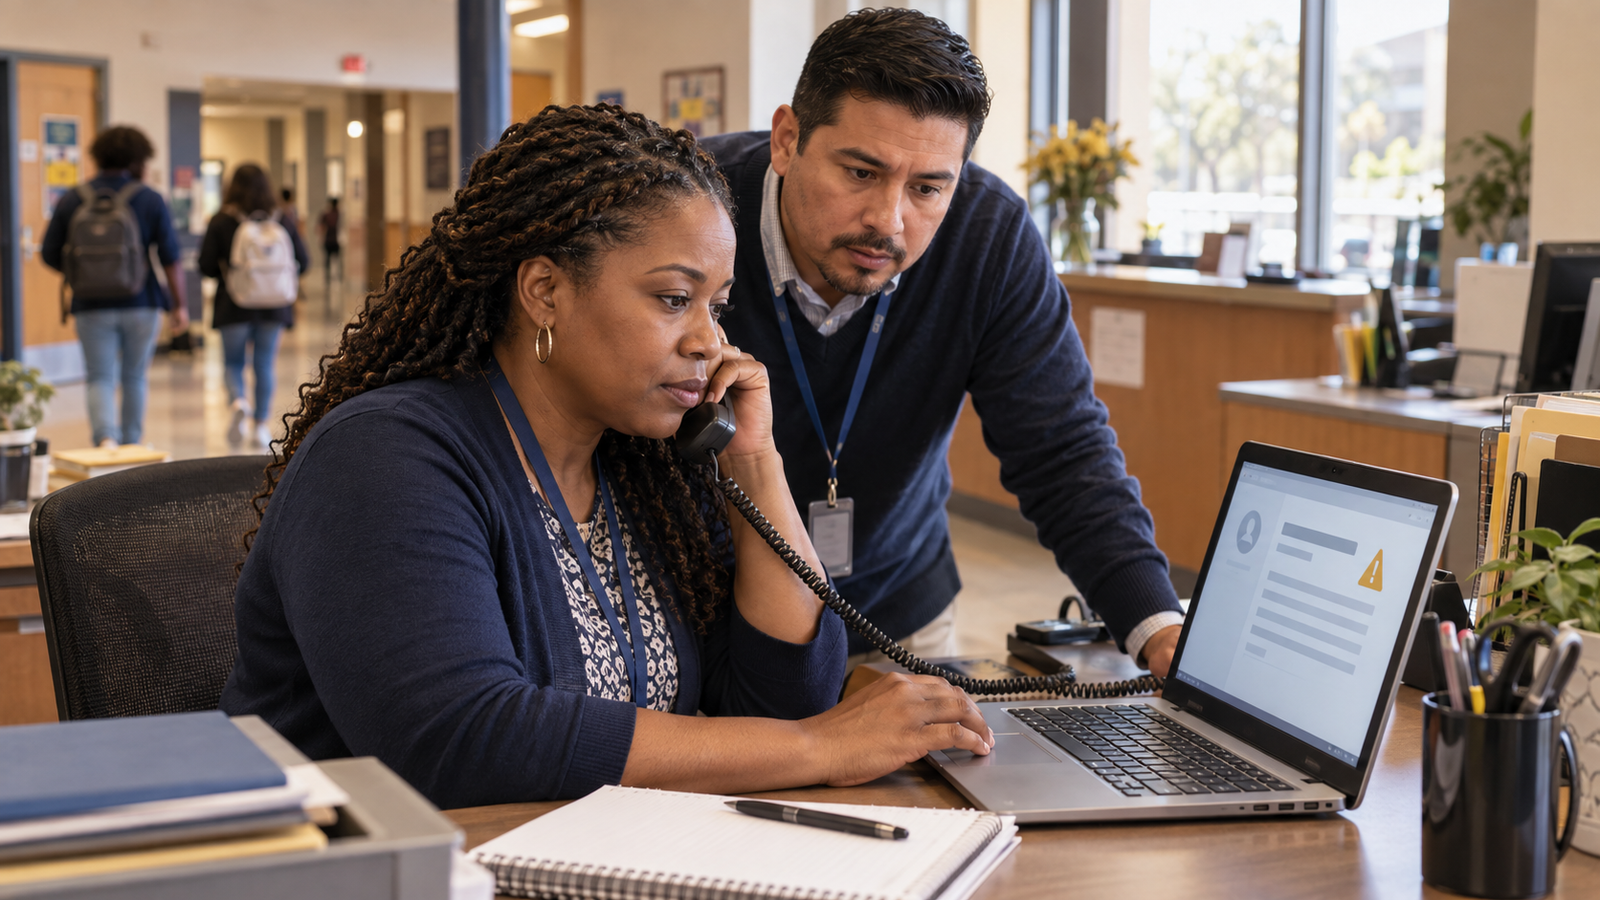
Social engineering in schools can begin with a request that seems perfectly ordinary.
Imagine a school secretary receiving an email that appears to come from the principal. It asks for a student contact list before an afternoon meeting. The wording sounds familiar, and the sender explains that the principal cannot talk right now.
The request is fake. Between a ringing phone and parents waiting at the counter, though, it could pass for another task that needs to get done.
Social engineering exploits trust to persuade someone to share sensitive information, send money, or provide access. Deception that gains a person’s confidence to obtain information or commit fraud is central to the National Institute of Standards and Technology’s definition.
Artificial intelligence can make these requests more convincing. Schools need to address that risk in staff training, classroom lessons, and the procedures employees follow every day.
What AI changes
Social engineering predates generative AI. Impersonating a trusted colleague or pressuring someone to act quickly requires no sophisticated technology.
AI can make the deception easier to produce and harder to recognize. In a December 2024 public advisory, the FBI warned that criminals were using generative AI to create believable messages, reduce spelling and grammatical errors, and generate images, audio, and video for fraud schemes.
For anyone taught to spot scams by looking for awkward wording, that is a significant limitation. A polished message still needs to be checked when it asks for sensitive information or an unusual action.
The same applies to a familiar voice. The Federal Trade Commission warns that scammers can use a short recording to clone a loved one’s voice. It advises verifying the story by calling that person at a number already known to be theirs.
For a school, a voice resembling an administrator’s should not be enough to authorize an unusual payment or release sensitive information.
How it can show up during the school day
Consider a teacher receiving a false warning that their account will be suspended unless they sign in through a supplied link. That is a phishing attempt: a deceptive message intended to trick the recipient into taking an action, such as entering a password on a fake website.
A business office could receive a fraudulent request to change a vendor’s payment information. A student might be offered a scholarship that requires an immediate fee. Each gives the recipient a reason to hurry, making verification feel like an obstacle to finishing the task.
The FTC describes scholarship scams that falsely announce a student’s selection, demand upfront payments, or request financial information. Counselors can use these examples when helping students prepare for college applications.
A message that appears to come from a principal, coach, or counselor carries weight. Staff and students should feel comfortable questioning an unusual request from someone they respect. Otherwise, the sender’s apparent authority can become a reason to skip checking.
Teach students to examine the request
Social engineering fits into digital citizenship, media literacy, and college and career preparation. A short classroom exercise can give students practice responding when they feel rushed or uncertain.
A teacher might present a fictional message claiming that a scholarship will disappear unless the student pays a processing fee that afternoon. Ask students:
- Who is the sender claiming to be?
- What are they asking me to do or reveal?
- How are they trying to influence my decision?
- How could I check the request independently?
Have students explain their next step and identify whom they would contact. They might consult a counselor, find the organization’s official website independently, or involve a parent before sharing information. The exercise should leave them with a response they can use.
Younger students could examine a message promising a game reward in exchange for a password. Older students could discuss employment offers or messages that impersonate classmates.
Teachers can use a district-approved AI tool to prepare fictional examples at different reading levels. Use invented identities, keep real student information out of the prompts, and review the output before sharing it. Keep the activity focused on discussing examples, with no deceptive messages sent to classmates or collection of actual passwords.
Make verification part of school procedures
Staff need practice with requests they encounter in their jobs. Office staff could discuss a questionable records request. Employees who handle purchasing could work through a supposed vendor payment change and identify how they would verify it.
District procedures should make the next steps clear:
- Verify changes to payment or payroll information through an established contact method before making the change.
- Follow the school’s authorization process before releasing student records, including when a request appears to come from a senior administrator.
- Open familiar services through a saved bookmark or approved app when checking an unexpected account warning.
- Give staff a clear way to report suspicious requests and get help promptly.
Replying to a suspicious message or calling the number supplied in it may lead back to the same person. The FTC recommends contacting an organization through a phone number or website already known to be genuine.
Administrators need to follow the same procedures. Regularly asking employees to bypass checks because something is urgent makes it harder for staff to recognize when a request crosses a line.
Families also need to know where to confirm school payment requests and unexpected messages involving their children. Include those directions in routine communications, in the languages families use.
Make it easy to ask for help
Even a well-trained employee can be deceived. The United Kingdom’s National Cyber Security Centre cautions that people cannot be expected to identify every phishing attempt. It recommends combining education with technical protections and preparation for incidents.
Schools should pair training with email filtering, multifactor authentication, and access limited to what each role requires. Employees also need a clear reporting process if they realize they may have shared information or followed a suspicious link.
The NCSC warns that fear of punishment can discourage reporting. Staff should feel able to say, “I think I made a mistake,” immediately. That gives the school a chance to respond before more damage occurs.
At the next staff meeting, return to the secretary’s situation. Where should that employee go to confirm the request, and does everyone in the office know the process?
A school secretary who pauses to verify a request should know the principal will support that decision.
For what a school should do once a scam has worked, see edCircuit’s Social Engineering in Schools: What to Do After a Scam Works.
Subscribe to edCircuit to stay up to date on all of our shows, podcasts, news, and thought leadership articles.
Related reading
More on Artificial Intelligence